
Microsoft SC-200 Exam : Microsoft Security Operations Analyst

- Exam Code: SC-200
- Exam Name: Microsoft Security Operations Analyst
- Updated: Nov 13, 2026
- Q & A: 435 Questions and Answers
About Microsoft SC-200 Exam Questions
A Microsoft certification opens doors to better roles, better salaries, and better company. The Microsoft Security Operations Analyst exam guards those doors, and the 435 practice questions at DumpsActual are the key-cutting service.
Microsoft SC-200 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Mitigate threats using Microsoft Defender for Cloud | 25-30% | - Respond to cloud security incidents
|
| Mitigate threats using Microsoft Sentinel | 40-45% | - Automate response and orchestration
|
| Mitigate threats using Microsoft 365 Defender | 25-30% | - Investigate and respond to threats
|
SC-200 Exam FAQ: Reduce Your Risk, Read This First
Microsoft Security Operations Analyst is an official Microsoft exam, identified by exam code SC-200. Passing it earns the Microsoft Certified: Security Operations Analyst Associate certification at the Associate level. It also relates to Microsoft Certified: Security, Compliance, and Identity Fundamentals, Microsoft Certified: Cybersecurity Architect Expert, Microsoft Certified: Azure Security Engineer Associate. Certifications like this one remain a reliable route to standing out: they prove ability in a way resumes alone cannot.
The Microsoft Security Operations Analyst exam contains 40-60 (varies) questions to complete within 100-120. The candidates who run out of time are usually the ones who never practiced against a clock. The DumpsActual software engine lets you limit your test time exactly like the real exam, exposing pacing weaknesses while they are still free to fix.
You need 700 (out of 1000) to pass Microsoft Security Operations Analyst, and the official registration fee is USD 165 (varies by region). Retakes charge the full USD 165 (varies by region) again, which makes failing a genuinely expensive outcome. Reduce that risk the rational way: practice with the DumpsActual questions until your scores sit consistently above the requirement, then book.
No formal prerequisites required, but familiarity with Microsoft 365, Azure, and security operations is recommended.
Vendor requirements change from time to time, so verify the current conditions before registering via the official exam page.
Registration for Microsoft Security Operations Analyst runs through the official channels below.
One practical note: the exam is delivered Online proctored or in-person at authorized testing centers (Pearson VUE)..
Microsoft recommends the following training for Microsoft Security Operations Analyst candidates.
Whatever training you take, anchor it with the 435 practice questions in the DumpsActual SC-200 package, each with a detailed explanation that turns every mistake into a lesson.
Yes. You can download the free demo of the Microsoft Security Operations Analyst questions before you buy, and after purchase you have the right to one year of free updates. When your product expires, extending the update service costs 50% of the regular price. Three versions, PDF, software, and online APP, let you study the way that suits you.
A 100% money-back guarantee protects you under clear conditions. Take the Microsoft Security Operations Analyst exam within 60 days of purchase; if you fail, you can claim a full refund, provided the exam matches your product. Attempts within 3 days of purchase are ineligible, as are downloaded-but-unused products, free materials, and expired orders; the candidate name must match the payer name. Submit a scanned enrollment slip and the official Score Report PDF within 2 days of the exam, and claims are processed within 7 days. Alternatively, exchange for two other exam products of equal value, free, while keeping the update service on your original purchase.
Delivery is instant: files unlock for download at payment and are automatically emailed within one minute. If nothing arrives within 2 hours, check spam and contact customer service, available 24/7. Installation is unlimited across your computers.
The Microsoft Security Operations Analyst syllabus divides into 3 domains. The leading areas are Mitigate threats using Microsoft Defender for Cloud (25-30%), Mitigate threats using Microsoft Sentinel (40-45%), and Mitigate threats using Microsoft 365 Defender (25-30%). The complete outline is published above; knowing your shortcomings starts with knowing the syllabus.
Microsoft Security Operations Analyst Sample Questions:
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You use Azure Security Center.
You receive a security alert in Security Center.
You need to view recommendations to resolve the alert in Security Center.
Solution: From Security alerts, you select the alert, select Take Action, and then expand the Mitigate the threat section.
Does this meet the goal?
- A. Yes
- B. No
Correct Answer: A 🗳️
Explanation: Only visible for DumpsActual members. You can sign-up / login (it's free).
You have a Microsoft Sentinel workspace named Workspace1 that is connected to the Microsoft Sentinel data lake and contains a table named Table1.
You need to create a scheduled KQLjob named Job1 that runs hourly, queries data across multiple Microsoft Sentinel workspaces, and writes the output of Job1 to Table1.
What should you do?
- A. Add a project statement to Job1.
- B. Ensure that the output of Job1 matches the schema of Table1.
- C. Append the _KQL_CL suffix to Table1.
- D. Assign the Microsoft Sentinel Reader role on Workspace1 to the managed identity of Job1.
Correct Answer: B 🗳️
Your network contains an on-premises Active Directory Domain Services (AD DS) domain that syncs with an Azure AD tenant.
You have a Microsoft Sentinel workspace named Sentinel1.
You need to enable User and Entity Behavior Analytics (UEBA) for Sentinel1 and collect security events from the AD DS domain.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.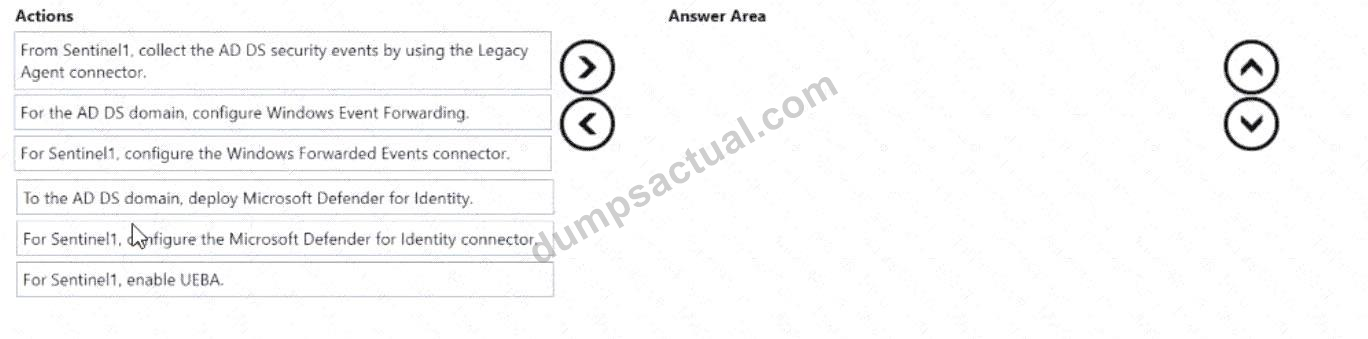
Correct Answer:

Explanation:
To enable User and Entity Behavior Analytics (UEBA) in Microsoft Sentinel and collect Active Directory Domain Services (AD DS) security events, the integration relies on Microsoft Defender for Identity (MDI).
Defender for Identity monitors on-premises domain controllers and provides deep identity-based telemetry that Sentinel consumes for behavioral analytics and threat detection.
Here's the correct sequence explained step-by-step:
Deploy Microsoft Defender for Identity on the AD DS domain
Defender for Identity sensors must be installed on each domain controller (or dedicated server) in your on- premises AD DS environment.
This step enables continuous monitoring of AD activities like logons, Kerberos authentications, and LDAP queries.
Microsoft documentation states:
"To collect and analyze AD DS activities for UEBA, deploy Microsoft Defender for Identity sensors in your domain controllers." Configure the Microsoft Defender for Identity connector in Microsoft Sentinel In the Sentinel workspace (Sentinel1), go to Data connectors # Microsoft Defender for Identity # Connect.
This connector ingests identity-related alerts and telemetry from Defender for Identity into Sentinel's Log Analytics workspace.
It allows Sentinel to correlate identity-based security data with other sources for threat detection and investigation.
Enable UEBA in Microsoft Sentinel
After integrating MDI, enable UEBA in Sentinel's configuration settings.
UEBA uses identity data (from MDI and Azure AD) and other logs to build behavioral baselines and detect anomalies such as lateral movement or privilege escalation.
Microsoft documentation notes:
"To start analyzing user and entity behaviors, enable UEBA after connecting identity data sources such as Defender for Identity." Other actions listed (such as using legacy connectors or Windows Event Forwarding) are outdated or unnecessary when using MDI and Sentinel's built-in connectors.
You have a Microsoft 365 subscription.
You have 1,000 Windows devices that have a third-party antivirus product installed and Microsoft Defender Antivirus in passive mode.
You need to ensure that the devices are protected from malicious artifacts that were undetected by the third - party antivirus product.
Solution: You configure endpoint detection and response (EDR) in block mode.
Does this meet the goal?
- A. Yes
- B. No
Correct Answer: A 🗳️
Explanation: Only visible for DumpsActual members. You can sign-up / login (it's free).
You have a Microsoft Sentinel workspace named sws1.
You need to create a query that will detect when a user creates an unusually large numbers of Azure AD user accounts.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation:
First table: BehaviorAnalytics
Joined table: AuditLogs
To detect when a user creates an unusually large number of Azure AD user accounts in Microsoft Sentinel, you should leverage UEBA signals from the BehaviorAnalytics table and enrich them with Azure AD audit data from AuditLogs. The BehaviorAnalytics table contains UEBA-derived insights (for example, the ActivityInsights flag and UsersInsights) and normalized activity fields such as ActionType (e.g., " Add user " ). Filtering BehaviorAnalytics for ActionType == " Add user " and ActivityInsights has " True " targets activities that the UEBA engine already assessed as anomalous, reducing noise and focusing on outliers.
Then, join these anomalies to the AuditLogs table to pull authoritative Azure AD audit details (target object, initiator, correlation, and operation context). This combination aligns with Sentinel guidance: use BehaviorAnalytics for anomaly detection and AuditLogs for the Azure AD operational record. Sorting by TimeGenerated and projecting user and insight fields completes the hunting query so analysts can review who triggered unusual "Add user" bursts and with what context.
Therefore, complete the query by selecting BehaviorAnalytics as the primary dataset and AuditLogs in the join (...).
Viewing page 1 out of 87 pages.
Viewing questions 1-5 out of 435 questions.


Related Exams
Related Certifications
Over 69163+ Satisfied Customers
Related Blogs
- [Q17-Q41] Microsoft SC-200 Practice Verified Answers - Pass Your Exams For Sure! [2026]
- Pass Your Microsoft Certified: Security Operations Analyst Associate SC-200 Exam on Nov 18, 2024 with 283 Questions [Q150-Q173]
- Prepare for your exam certification with our SC-200 Certified Microsoft [Q66-Q83]
- [2023] Pass your SC-200 exam with this 100% Free SC-200 Braindump [Q81-Q102]
- More ...
 801 Customer ReviewsCustomers Feedback (* Some similar or old comments have been hidden.)
The SC-200 exam questions have helped me to get a easy success on my SC-200 exam this Monday. Thanks!
Dominic

I used SC-200 study dumps as my only tool for my exam, I passed it easliy, that is why I suggest that for any kind of certification training select DumpsActual.
Belinda

The SC-200 exam file really covers exam questions in details with relevant practical content. I was depending on it for my exam and got a pass at the first attempt. Great!
Don
Great that I can get you! Thank you for the great SC-200 study materials.
Rose
Please believe me when I say that SC-200 materials are the best source for getting the Microsoft training material on the internet. It's simply great!
Eden
I studied DumpsActual Microsoft SC-200 exam Guide whole heartedly and was surprised to see that this small guide surpassed all available sources with me in its usefulness. It consisted Complete Return
Martina
I studied for the SC-200 certification exam using the pdf question answers by DumpsActual. Made my concepts about the exam very clear. Highly recommended.
Alvis
I am from Africa and so appreciate that you help with SC-200 exam braindumps, which are saving money and time. They are super easy to use, thanks!
Christian
I passed this SC-200 exam easily.
Max
I passed the SC-200 exam with the Software version which they told can simulate the real exam. For I always forget the time and i have no idea about the content. It really helped to avoid these problems.
Bradley
I got SC-200 certified.
Harlan
Achieved amazing score in exam Microsoft SC-200 ! I wanted to get the best score and it came using DumpsActual unique and the most helpful exam dumps. I'm mesmerized Comprehensive Study Guide!
Betsy
QUALITY AND VALUE
DumpsActual Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
EASY TO PASS
If you prepare for the exams using our DumpsActual testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
TESTED AND APPROVED
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
TRY BEFORE BUY
DumpsActual offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
Our Clients




Our exam study dumps are compiled through several times of checking and verification, which are with the high pass rate up to 98%. All the actual questions & answers are selected and confirmed according to strict standards with assurance for 100% pass.
Latest Exam Questions
- Actual SPLK-5003 DumpsMay 28, 2022
- Actual Platform-App-Builder DumpsMay 28, 2022
- Actual DP-420-KR DumpsMay 28, 2022
- Actual CAS-005-JPN DumpsMay 28, 2022
Contact Us
From Monday to Saturday
Support: Contact now
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Copyright © 2026 DumpsActual NETWORK CO.,LIMITED. All Rights Reserved. All trademarks used are properties of their respective owners. Privacy Policy